

In distributed systems, duplicate requests are not an edge case—they are inevitable. Network retries, client timeouts, message redelivery, and partial failures all lead to the same operation being executed more than once. Without proper safeguards, these duplicates cause corrupted data, double charges, inconsistent state, and hard-to-debug production incidents.
This is why idempotency is a foundational requirement for reliable distributed systems—especially in Azure-based architectures that rely heavily on retries, messaging, and asynchronous processing.
Why Idempotency Matters in Azure Systems
Azure services are designed for resiliency, not guarantees of single execution. Message queues deliver at least once, APIs may be retried automatically, and clients often resend requests when they don’t receive a response in time. From the platform’s perspective, this is correct behavior. From the application’s perspective, it can be disastrous if operations are not idempotent.
In practical terms, idempotency ensures that performing the same operation multiple times produces the same result as performing it once. The system becomes safe under retries and failures—exactly the conditions distributed systems operate in.
Where Idempotency Is Commonly Required
In real Azure implementations, idempotency is critical in:
- API endpoints handling commands (payments, orders, registrations)
- Message consumers processing Service Bus or Event Grid events
- Background jobs triggered by retries
- Workflow steps in long-running processes
Any operation that changes state must assume it may run more than once.
A Practical Azure Idempotency Pattern
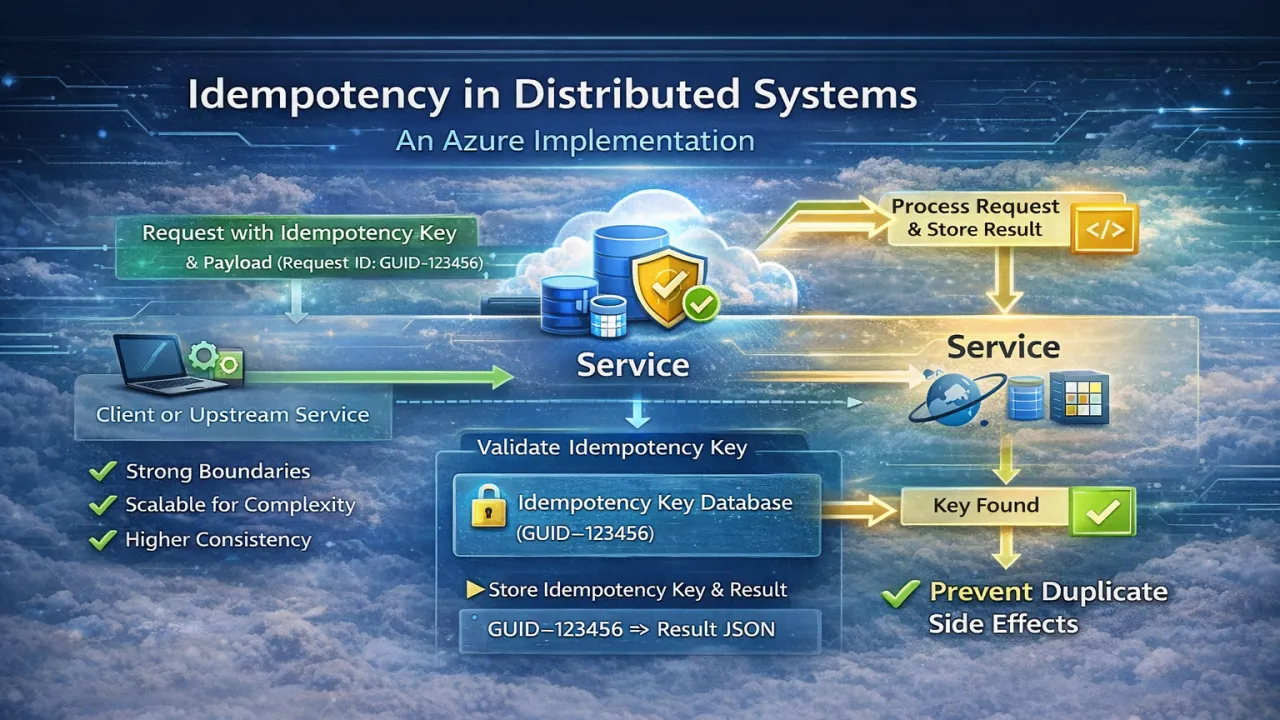
A common and effective pattern in Azure systems is idempotency keys.
When a client or upstream service sends a request, it includes a unique idempotency key (often a GUID). The service then:
- Checks whether the key has already been processed
- If yes, returns the previous result
- If no, processes the request and stores the result with the key
This record is stored in a durable store such as Azure SQL, Cosmos DB, or Table Storage. The key becomes the source of truth that prevents duplicate side effects.
Idempotency in Messaging Scenarios
Azure Service Bus guarantees at-least-once delivery, not exactly-once processing. This means consumers must assume duplicate messages will arrive.
In production systems, consumers typically:
- Use the message ID or a business correlation ID
- Store processed message IDs
- Ensure side-effects (database writes, external calls) are safe to repeat
The goal is not to stop duplicates—it’s to neutralize their impact.
What Idempotency Is NOT
A common misconception is that idempotency is handled by:
- Disabling retries
- Relying on transactions alone
- Assuming infrastructure guarantees uniqueness
None of these work reliably in distributed systems. Idempotency is an application-level responsibility, not something the platform can fully solve for you.
Trade-offs and Design Considerations
Implementing idempotency introduces its own considerations:
- Storage overhead for processed keys
- Cleanup strategies for old records
- Slight increase in write latency
- Clear definition of what “same request” means
These trade-offs are minor compared to the cost of corrupted state, customer impact, and emergency fixes.
Final Thoughts
Idempotency is not an optimization—it’s a correctness requirement.
In Azure-based distributed systems, retries, redelivery, and partial failures are normal. Systems that don’t account for this will eventually fail in unpredictable and expensive ways. Systems that embrace idempotency behave calmly under pressure, recover cleanly, and scale safely.
If your system cannot tolerate duplicate execution, it is not production-ready.
Idempotency turns unreliable networks and retries from a liability into a strength—and it’s one of the most practical design decisions you can make in modern Azure architectures.